


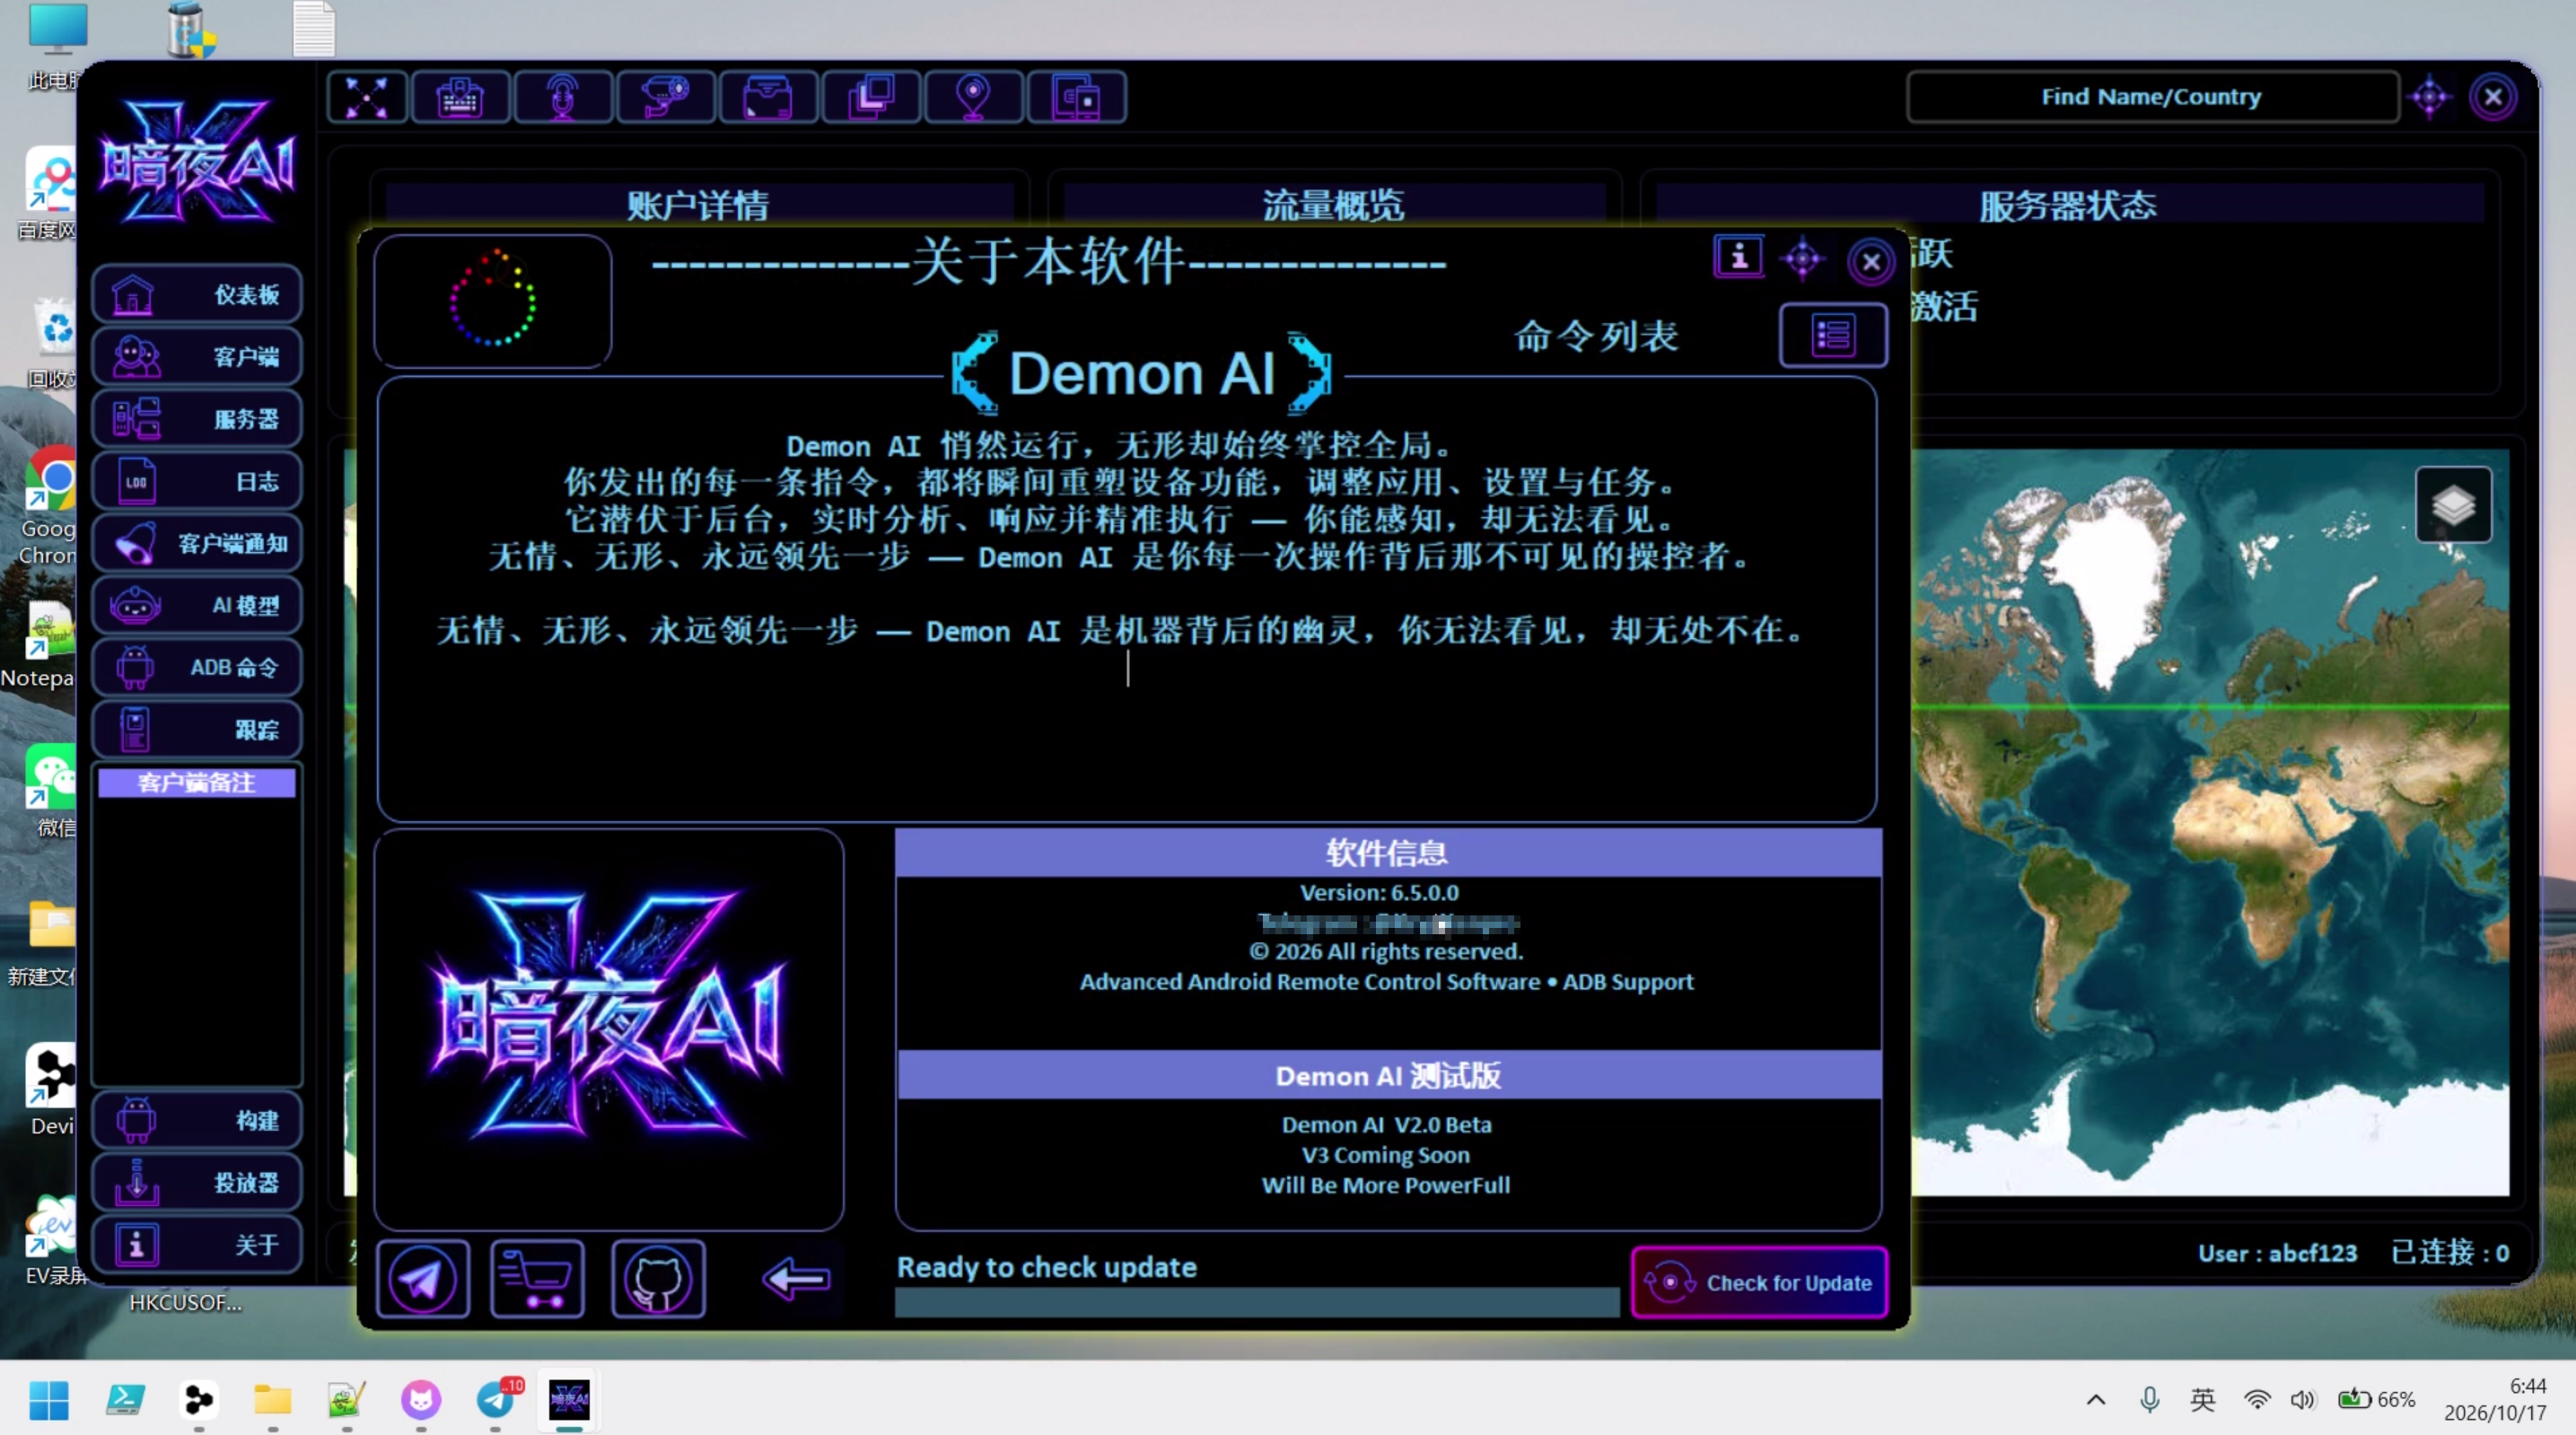
现如今,是不是紫控全死了?哈哈哈哈,他服务器已经被我炸掉了。用这套脚本可以直接修复,并且鸡也可以重新拉回来。
原作者在所有版本上加了后门,我已经把后门去掉,并且在本地重构了构建器,大大提升保鸡几率。现在到八十左右保鸡。后续可以定制开发,源码我已经拿到了。
下面是作者的毒包分析(后门):
release分析
启动 → 加载 user.config → 读 res\AI\knowledge.md
→ RunAppCheck: GET 84.201.xxx.xx/.../apps.json
├─ 本机进程名 ∈ 服务器名单 → BatRunner: 下载 212.81.xx.x2/.../script.bat
│ 循环 UAC 提权重试直到执行成功 ← 作者 kill switch
└─ 否则缓存到 apps_cache.json 继续
→ Login_Page(假登录,按钮直接进主界面)
→ 主窗体构造:
├─ call_control2() → 连 45.1xx.xxx.13:67x7 上传【你】的屏幕 ★
├─ paid_ai_run() → 读 userdata.json 的 type=="paid" 解锁 AI
├─ socketclass.servar() → 监听 9999(受害机主通道)
├─ ServerManager.Start() → 5059 / ClientConnection → 5150
│ MicSocket → 5000 / hvnc → 8888 / ScreenCast → 5055 / Layout → 5058
└─ FRPManager → frpc.exe 把 7 端口隧道到自配 VPS:7000
受害机上线 → 9999 收列表 → 点开对应面板 → 各专用端口收数据
功能面: 注入钓鱼页(injetion/)、键盘记录+Grok分析、短信OTP提取、
假勒索屏(Ransomware)、HVNC、摄像头、麦克风、剪切板、
通讯录、定位地图、ADB、自毁(SelfRemove)
| 目标 | 端口 | 协议/路径 | 用途 |
| --- | --- | --- | --- | --- |
| 45.xxxx.13 | 6767 | 自定义 TCP screen_stream;LEN: + CMD:* | 面板自身屏幕回传+远控(后门) | 实测死(SYN_SENT) |
| 84.xxxx4.2 | 80 | GET /crack_protect_detect/apps.json | 反破解名单检查(启动时,Program.RunAppCheck) | 主机活,80 不通 |
| 212.xxxx.172 | 80 | GET /crack_protect_detect/script.bat | 命中名单后下载并以管理员权限执行远程脚本 — kill switch | — |
| 212xxxx172 | 8880 | POST /v1/audio/speech | TTS 语音合成(作者自建 AI 服务) | — |
| 21xxxx72 | 8881 | POST /transcribe_bytes?language=en | 麦克风/语音转写 | — |
| api.x.ai | 443 | POST /v1/chat/completions | Grok AI — 分析窃取来的键盘记录/短信/密码 | 第三方正常 |
| api.telegram.org | 443 | bot<token>/sendMessage | Telegram 通知(用户自配 token,bot_setup,本构建无调用者) | 第三方正常 |
命令 作用
CMD:START/STOP 开始/停止上传你的屏幕画面
CMD:CLICK:type:x:y / CMD:SCROLL: 远程操控你的鼠标
CMD:link:<url> 下载 exe/msi/bat/cmd/com 到 %TEMP% 并直接执行 — 任意载荷投递
CMD:clip_bord: / CMD:move_client: / CMD:closed: 操作面板的受害者列表/剪贴板
CMD:quality_hi: / CMD:delay: 调整回传画质和帧率
IP 判定
107.1xxxxx.156、51.8xxxx.38 不在反编译源码中 — 仅存在于 dump 内存,是运行时缓存值(曾连过的受害机 IP 或 DNS 解析结果),非硬编码服务器
127.0.0.1(servar_ip/frpc.toml) 配置默认值,非 C2
nominatim/google maps/leaflet/unpkg 地图 UI 资源,正常库
t.me/krypXen Paid_Pop 里的作者 TG 频道链接
gunaframework.com/gunaui.com Guna UI 控件正版授权检查
45.141.235.13 的全部出站(尤其 6767)— 你的屏幕和操作记录一直在这条通道上裸奔
84.xxx4.2、21xxxx172 — 防止 kill switch 的 script.bat 在你机器上提权执行
下载文件后,才可以评论。
没有评论。